
Tag: #OnlineSafety


Google Play Store removed apps that were secretly stealing user data, exposing millions of Android devices to security threats. These malicious apps contained KoSpy spyware, linked to North Korean hacking group APT37 (ScarCruft). They remained undetected for over two years, collecting sensitive information such as call logs, messages, and GPS locations. If any of these […]
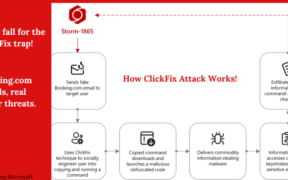
The ClickFix attack is a sophisticated phishing campaign that impersonates Booking.com to deliver infostealers and Remote Access Trojans (RATs) to hospitality workers. This phishing attack specifically targets individuals in hospitality organizations in North America, Oceania, South and Southeast Asia, and Northern, Southern, Eastern, and Western Europe, who are most likely to work with Booking.com. Attackers […]

A malicious Python Package Index (PyPI) package named “set-utils” has been discovered stealing Ethereum private keys by intercepting wallet creation functions and exfiltrating them via the Polygon blockchain. Disguised as a utility for Python, it mimics popular packages like “python-utils” and “utils,” which have millions of downloads. Researchers from the developer cybersecurity platform Socket identified […]